Vulnerability Discovery and
Remediation - Together at Last
Use Action1 vulnerability management and remediation software to identify CVEs, prioritize what requires action, and remediate with pre-tested patches or documented compensating controls. Set up in 5 minutes, launch a free vulnerability scan, then remediate CVEs at no cost for your first 200 endpoints.
Trusted by many Fortune 500 companies
99%Patch success rate10M+Endpoints protected5K+Customers


Discover vulnerabilities. Remediate
them. Without switching tools.
Finding a vulnerability is only the beginning. Exposure remains until the
vulnerability is patched and the outcome is verified. Action1 connects detection
and remediation in one workflow, giving IT teams a clear view of what has been
addressed and what requires action.
Discover and prioritize
Identify OS and application vulnerabilities, not only those with available patches, across Windows and macOS endpoints. Prioritize using CVSS scores, CISA KEV status, affected endpoints, and SLA deadlines.
Remediate
Deploy verified Windows, macOS, Linux, and supported third-party updates through controlled automation. When no suitable patch is available, apply a compensating control, such as running a script or changing a firewall rule.
Verify and document
Confirm successful patch deployment, maintain records of compensating controls, track remaining exposure, and preserve audit-ready evidence.


Why IT teams choose
Action1 for vulnerability
detection and
remediation
No more passing CVEs from a vulnerability scanner to a ticket queue and then to a separate patching tool. Action1 connects vulnerability discovery, risk-based prioritization, and remediation in one workflow, so IT teams can move from a detected CVE to a verified patch deployment or documented compensating control without manual handoffs.
Integrated vulnerability discovery, prioritization and remediation
Identify and fix OS and supported third-party application vulnerabilities across managed Windows, macOS and Linux endpoints. Combine Action1's native vulnerability detection with CVE and asset data received from vulnerability management and endpoint security platforms such as Rapid7, Tenable, CrowdStrike, and Qualys. Prioritize what to address first using CVSS scores, CISA KEV status, and SLA deadlines, then deploy a verified patch or apply a compensating control.
Cloud-native by design
Detect and remediate vulnerabilities across remote, distributed, and off-network endpoints from a browser-based console. When a suitable patch is available, deploy the verified update without VPN-dependent workflows or on-premises patch servers. When patching is not possible or an update does not pass Action1 verification, document the compensating control implemented by your team and continue tracking the vulnerability in Action1.
Free vulnerability scan across unlimited endpoints
Assess vulnerabilities across an unlimited number of supported Windows and macOS endpoints at no cost. Then continue with ongoing vulnerability detection, remediation, and full platform functionality free forever for your first 200 endpoints, with no expiration date.
Pre-tested patches with PatchAssurance™
For supported third-party applications, Action1 provides a patch catalog that is curated, tested, verified, and maintained by in-house experts. Only patches that pass Action1 verification are approved for deployment. This helps IT teams avoid deploying unverified updates or relying solely on packages from public repositories such as WinGet or Chocolatey.
Controlled patch rollouts with zero disruption
Use approval policies, maintenance windows, and deployment rings to test and stage updates. Promote patches only after they meet defined success criteria, reducing the risk that a problematic update causes widespread operational disruption.
Audit-ready remediation evidence
Track successful, failed, and pending patch deployments, remaining exposure, SLA status, and remediation history. Maintain records of compensating controls - including what was done, who recorded it, and when - to provide clear evidence for audits, security reviews, and stakeholder reporting.
Security built into the platform
Remediate vulnerabilities through a secure, resilient platform. Action1 treats security as a core product capability, helping reduce the risk that the platform itself becomes a source of exposure or an entry point into your environment.
Global data residency for local compliance
Keep your Action1 data in the region that meets your organization's residency and regulatory requirements, with hosting available in the USA, UK, Europe, and Australia. Action1 can rapidly expand to new regions as local requirements evolve.
Bring vulnerability
scanning and remediation
together
Action1 works alongside the vulnerability management and endpoint security platforms your team already uses. Connect CVE data from Rapid7 InsightVM, Tenable, CrowdStrike Falcon Spotlight, Microsoft Defender for Endpoint, and Qualys with devices managed in Action1.
Correlate vulnerabilities with affected endpoints, identify coverage gaps, and prioritize remediation using CVSS scores, CISA KEV status, ransomware associations, affected endpoints, and SLA deadlines. Then determine the appropriate remediation path: deploy a verified patch or apply and document a compensating control.

Action1 in the analyst spotlight

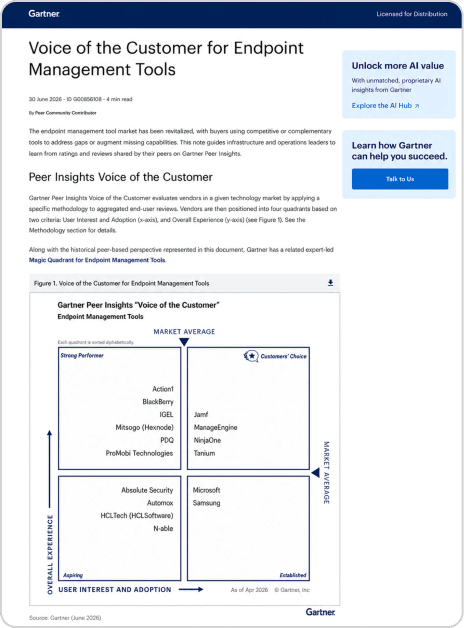
Action1 named Strong Performer in Gartner® Peer Insights™ Voice of the Customer for Endpoint Management Tools, 2026.
View full report
